Adopt outcome-led governance: executive oversight, one client-side CX owner, a joint steering committee, outcome-focused KPIs, and contract terms that require resilience. Regulators such as the FFIEC and FDIC, the ISO 37500 standard, and Gartner all point the same way. Your levers are KPIs, SLAs, monitoring, and business continuity.
TL;DR:
- Name one client side CX owner, pair them with an empowered vendor lead, and review strategy quarterly while working groups resolve weekly operational issues.
- Keep loyalty programs, VIP support, and critical escalations within your organization; outsource documented, repeatable tasks, and require auditable controls for regulated or high risk work.
- Track first contact resolution, customer effort, resolution quality, and retention signals; treat handle time and answer speed as staffing guardrails, not performance targets.
- Put tested continuity plans, audit evidence, escalation contacts, and recovery expectations in writing; assign each finding an owner and deadline for steering committee review.
Table of Contents
- How should you structure governance for an outsourced CX team?
- What should outsourced CX governance control and measure?
- What do regulators expect from third-party risk governance?
- Which KPIs and scorecards should you use?
- Which contract and SLA clauses make governance enforceable?
- What does day-to-day oversight look like?
- How do you govern for improvement, not just compliance?
- Where can you find the supporting resources behind this guidance?
- What trade-offs do you accept when outsourcing CX?
- How does Altiam CX support governance-ready outsourced CX?
- FAQ
- Sources
How should you structure governance for an outsourced CX team?
Good governance starts with clear ownership. Without clear ownership, a provider may answer to multiple people and none of them owns the outcome. We recommend distinct governance tiers, each with a clear job:
- Board or executive oversight: sets risk appetite, receives oversight results, and approves renewals and material scope changes.
- Client CX owner: one named person accountable for outcomes, escalations, and the relationship. Not a committee.
- Vendor governance lead: the provider’s counterpart, with authority to commit resources and approve fixes.
- Joint steering committee: meets quarterly to review strategy, scorecards, risks, and the improvement backlog.
- Working groups: operations, quality, workforce, and compliance leads who meet weekly and solve tactical issues.
Allocate responsibilities in a simple RACI. Strategy stays with the executive sponsor and CX owner. Contract changes are owned by the CX owner with legal and procurement consulted. Incident response is run by the vendor lead, with the CX owner informed promptly. Compliance reporting belongs to your risk function, fed by the provider.
Put decision gates around key moments, including procurement, scope changes, escalations, and renewals. Each gate needs a named approver and written criteria. A scope change, for example, should require a documented impact on quality, cost, and risk before anyone signs.
What should outsourced CX governance control and measure?
Governance has to control the things that protect your customer relationships, and it has to measure them the right way. Gartner advises against outsourcing high-value CX activities such as loyalty programs, top-tier advocate support, and critical escalations, because they depend on deep institutional knowledge. It also cautions that leaning on efficiency SLAs like average handle time can mislead leaders, while outcome-led measures track loyalty more closely.
Use this checklist to decide what stays in-house and what goes to a partner:
- Is the activity brand-critical? If a mistake changes how customers see you, keep it close or govern it tightly.
- Does it drive loyalty or retention? Save-desk and VIP work usually belongs in-house.
- Is it high-risk or regulated? Keep it only if you can verify controls through audits and evidence.
- Is it repeatable and well documented? Standardized volume work is where outsourcing earns its keep.
- Can you describe good behavior in writing? If you can’t, you can’t govern it.
That last point matters more than most teams expect. Document behavioral standards for agents: scripting boundaries, escalation tone, de-escalation steps, and when to hand off to a human lead. Qualitative standards should be scored in QA, not left to impressions. When expectations are written down and scored, quality conversations with a provider stop being arguments and become reviews.
What do regulators expect from third-party risk governance?
Outsourcing moves the work, not the accountability. FDIC guidance states that boards and management remain responsible for third-party relationships, and that effective oversight requires written contracts, periodic reviews, qualified staff for monitoring, and reporting of oversight results to the board. Even if you are not a bank, this is a sound standard to borrow.
The FFIEC handbook adds a resilience angle: identify single points of failure, and if no alternative provider exists, define concrete options for continuing operations during a primary disruption. Governance artifacts to keep on file:
- Documented third-party risk assessments, refreshed on a set schedule
- SOC reports or equivalent audit evidence from the provider
- Written escalation protocols with named contacts and response times
- Business continuity plans that have been tested, not just filed
- A plan for moving work in-house or to another provider if the primary fails
Regulatory principle: Boards and management remain responsible for third-party relationships, so oversight results must reach the board.
During due diligence, request the latest audit reports, subcontractor lists, recovery test results, and incident history. Then route every audit finding into the steering committee with an owner and a due date. A finding that lives only in a report is a finding nobody fixed.
Which KPIs and scorecards should you use?
Build the scorecard around what customers experience, then add efficiency measures as guardrails. The outcome set we favor:
- First-contact resolution: did the customer need to come back?
- Customer effort score: how hard was it to get help?
- Quality of resolution: was the answer correct, complete, and compliant?
- Retention and loyalty proxies: repeat contact rates, cancellations after contact, and renewal signals tied to support interactions.
Efficiency metrics such as handle time and speed to answer still matter for staffing and cost. Treat them as boundaries, not goals. If handle time becomes the target, agents rush and repeat contacts climb.
Reflect this balance in your SLAs. Tie incentives to outcome metrics, keep penalties for clear failures, and avoid penalties that reward fast, shallow answers. Industry surveys point to governance maturity, monitoring cadence, and aligned commercial incentives as common success factors.
A workable reporting rhythm: daily operations metrics, weekly exception reports, monthly business reviews, and quarterly strategic reviews that feed the steering committee.
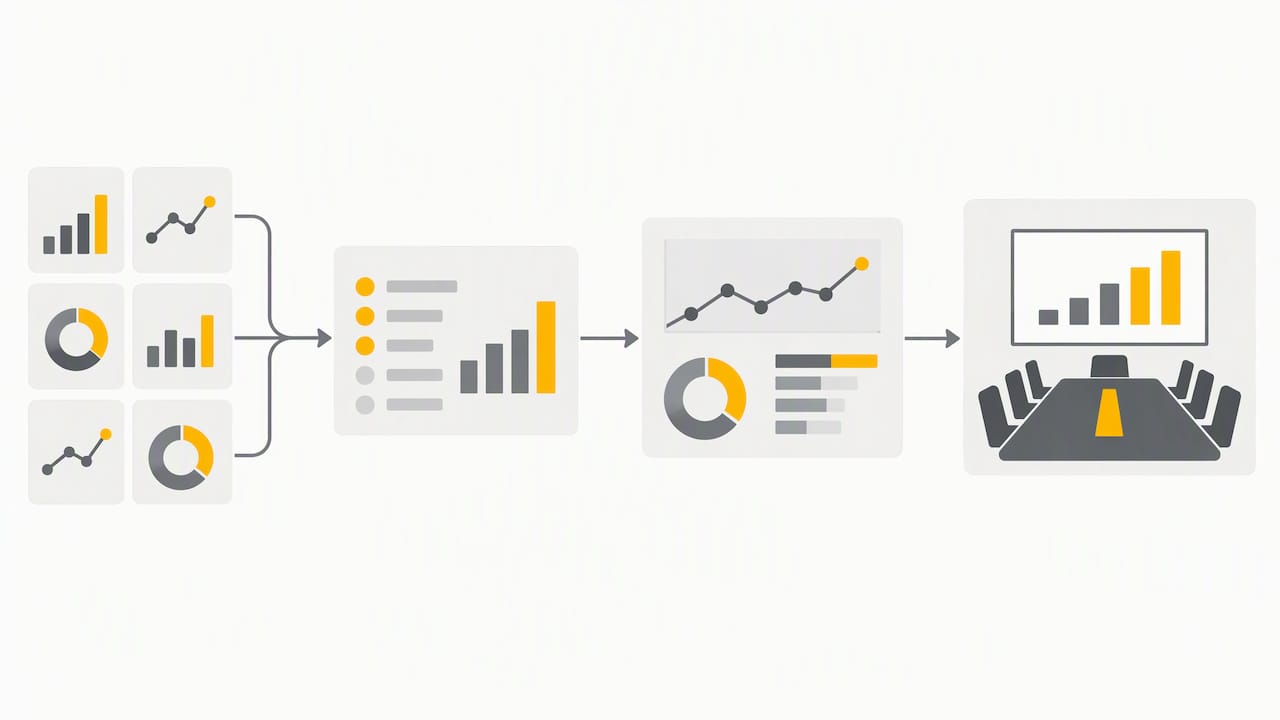
Pro Tip: Show trends over time on every scorecard. A single bad week is noise, but a slow slide in first-contact resolution is a governance problem.
Which contract and SLA clauses make governance enforceable?
Governance that isn’t written into the contract depends on goodwill. The FFIEC outsourcing guidance lists the oversight elements to cover: risk management, SLAs, pricing methods, ongoing monitoring, financial condition reviews of the provider, and business continuity provisions such as recovery-time expectations and periodic service reviews.
Structure SLAs around outcomes, with a baseline, a target, and incentive tiers above and below. Define every metric precisely, including the formula, the data source, and who measures it. Ambiguous definitions are where disputes start.
Clauses we would include:
- Business continuity: recovery time and recovery point expectations, participation in recovery tests, and portability to an alternative provider
- Audit evidence: SOC 1 or SOC 2 reports where relevant, plus your right to request more
- Subcontracting and assignment limits: no handoff of your work without written approval
- Audit rights: the ability to inspect processes, recordings, and QA data
- Escalation matrix: named roles, response times, and a path to executive level
- Remediation timelines: fixed windows to correct a missed target
- Termination triggers: material breach tied to customer-impacting failures, not only to missed averages
What does day-to-day oversight look like?
Strong governance feels boring in daily operations. Routines catch problems early, and runbooks keep a bad day from becoming a crisis. We use this sequence:
- Write runbooks for launches, policy changes, and incident response, each tied to the escalation protocol so everyone knows who acts and who gets told.
- Hold a daily operations standup covering volume, staffing, and anything that broke overnight.
- Run a weekly tactical meeting to review exceptions, quality trends, and open actions.
- Review SLAs monthly with the vendor lead, and bring the quarterly steering committee a summary.
- Sample QA continuously, using remote monitoring and a scored calibration process so your reviewers and the provider’s agree on what good sounds like.
- Spot-check through audits, including unannounced reviews of a few interactions.
- Feed every finding into coaching and corrective action, with an owner, a deadline, and a follow-up check.
The last step is the one teams skip. If QA results do not reach coaching within days, sampling becomes paperwork. Our nearshore CX process guide shows how this plays out in practice.
How do you govern for improvement, not just compliance?
Control and innovation can coexist. ISO 37500 frames governance as a mutual responsibility and recommends structures that let providers propose innovations and that stay flexible as business needs change. Your provider’s agents see failure patterns before your dashboards do, so give them a formal way to say so.
- Keep a joint improvement backlog where either side adds ideas, scored on business impact and risk.
- Set change-request gates with clear approvers, pilot criteria, success thresholds, and a rollback plan.
- Pilot narrow first: one queue, one team, or one channel before a wider rollout.
- Align mutual KPIs so the provider earns from improvements that raise resolution and loyalty, while brand-critical outcomes stay protected.
Planning ahead for journeys that cross channels helps too. Operational templates, such as journey orchestration planning, can shape how you prioritize backlog items.
Pro Tip: Reserve time in every monthly review for the provider’s top improvement idea. If it never comes up, your governance is discouraging it.
Where can you find the supporting resources behind this guidance?
Our recommendations draw on the regulatory and standards sources linked above, and on how we run managed nearshore CX programs day to day. We are a nearshore customer experience and managed team extension partner with bilingual teams, back-office support, and SOP management.
- Start with our CX outsourcing governance checklist to turn this framework into a working plan.
- Read why CX directors own outsourcing oversight for the executive side of accountability.
- Use our critical support function checklist before outsourcing sensitive work.
- Browse our nearshore customer experience services to see how these controls map to a managed team.
What trade-offs do you accept when outsourcing CX?
Scale and high-touch service pull in opposite directions. The more volume you hand a provider, the more you rely on process to keep the human quality customers remember. The trade-off I see most often is that leaders buy cost and coverage, then discover they never defined what a great interaction sounds like. My recommended priority is to write the behavioral standards first and score them every week, before you tune a single efficiency target. Our governance checklist is a practical next step.
— Daniela
How does Altiam CX support governance-ready outsourced CX?
Governance only works when your partner is built for it. Our nearshore teams are managed under documented SOPs, and we scale through managed team extension with bilingual agents who align with your culture. We report against outcome metrics, not just activity.
- Assess the governance readiness of your current outsourced CX setup.
- Get our governance checklist to benchmark your provider relationship.
See how it fits your operation on our services page, and tell us where you want stronger control.
FAQ
What is outsourced customer support?
Outsourced customer support means a third-party provider handles customer inquiries, technical help, or related back-office work on your behalf. You keep accountability for results, which is why governance matters. Regulators such as the FDIC say boards and management remain responsible for third-party relationships.
What is corporate governance in simple words?
Corporate governance is the set of rules, roles, and checks that decide who makes decisions and who is held accountable. For outsourced CX, it means naming owners, setting measurable expectations, and reviewing results on a schedule.
How do you govern an outsourced CX provider day to day?
Name one client-side CX owner, review scorecards on a fixed cadence, and sample quality every week. Put expectations in a written contract and send audit findings to a steering committee with owners and due dates.
What are the benefits of outsourcing the internal audit function?
Outsourcing audit work can bring specialist skills and added independence. The same rule applies as with CX: accountability stays with you, so you still need written scope, oversight, and reporting to the board.
Sources
- FFIEC IT Examination Handbook InfoBase - IV.A.5 Third-Party Service Providers
- Fdic
- ISO 37500:2014 - Guidance on outsourcing